Rate this post

[Sep 15, 2026] Prepare For The SC-300 Question Papers In Advance

SC-300 PDF Dumps Real 2026 Recently Updated Questions

Microsoft SC-300 Exam is ideal for IT professionals who are responsible for managing identity and access solutions in organizations of all sizes. This includes IT administrators, security analysts, and identity and access managers who are responsible for designing, implementing, and maintaining identity and access solutions based on Microsoft technologies. SC-300 exam is also recommended for individuals who are looking to advance their careers in the field of identity and access management, as it is a globally recognized certification that validates their expertise and knowledge in this area. With the increasing importance of identity and access management in today’s digital world, passing the Microsoft SC-300 Exam is a valuable achievement that can open up new career opportunities for IT professionals.


NO.102 You have an Azure Active Directory (Azure Azure) tenant that contains the objects shown in the following table.
* A device named Device1
* Users named User1, User2, User3, User4, and User5
* Five groups named Group1, Group2, Group3, Ciroup4, and Group5
The groups are configured as shown in the following table.

How many licenses are used if you assign the Microsoft Office 365 Enterprise E5 license to Group1?


NO.103 You have an Azure Active Directory (Azure AD) tenant that contains the groups shown in the following table.

For which groups can you create an access review?


NO.104 You have a Microsoft 365 tenant.
The Azure Active Directory (Azure AD) tenant syncs to an on-premises Active Directory domain. The domain contains the servers shown in the following table.

The domain controllers are prevented from communicating to the internet.
You implement Azure AD Password Protection on Server1 and Server2.
You deploy a new server named Server4 that runs Windows Server 2019.
You need to ensure that Azure AD Password Protection will continue to work if a single server fails.
What should you implement on Server4?


NO.105 You have 2,500 users who are assigned Microsoft Office 365 Enterprise E3 licenses. The licenses are assigned to individual users.
From the Groups blade in the Azure Active Directory admin center, you assign Microsoft 365 Enterprise E5 licenses to the users.
You need to remove the Office 365 Enterprise E3 licenses from the users by using the least amount of administrative effort.
What should you use?


NO.106 Your network contains an on-premises Active Directory Domain services (AD DS) domain that syncs with an Azure AD tenant. The AD DS domain contains the organizational units (OUs) shown in the following table.

You need to create a break-glass account named BreakGlass.
Where should you create BreakGlass, and which role should you assign to BreakGlass? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.107 You have an Azure Active Directory (Azure AD) tenant that contains the following group:
Name: Group1
Members: User1, User2
Owner: User3
On January 15, 2021, you create an access review as shown in the exhibit. (Click the Exhibit tab.)

Users answer the Review1 question as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

NO.108 You need to meet the planned changes for the User administrator role.
What should you do?


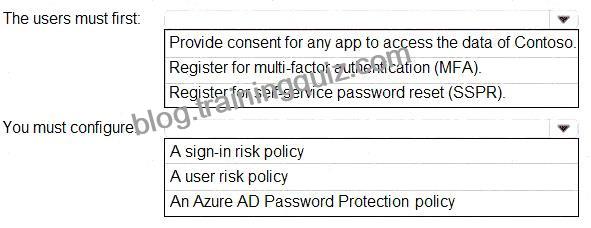
NO.109 You need to meet the technical requirements for the probability that user identities were compromised.
What should the users do first, and what should you configure? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.
NO.110 Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant.
All users must use the Microsoft Authenticator app for multi-factor authentication (MFA) when accessing Microsoft 365 services.
Some users report that they received an MFA prompt on their Microsoft Authenticator app without initiating a sign-in request.
You need to block the users automatically when they report an MFA request that they did not Initiate.
Solution: From the Azure portal, you configure the Fraud alert settings for multi-factor authentication (MFA).
Does this meet the goal?


NO.111 You have a Microsoft Entra tenant that contains an administrative unit named AU1. AU1 is configured for assigned membership.
The tenant contains the users shown in the following table.

For AU1, you update the following configurations:
. Membership type: Dynamic User
* Dynamic membership rule: (user.department -eq “hr”)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.

NO.112 You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Cloud Apps.
You discover that users connect to unsanctioned third-party apps.
You need to automatically identify and block the use of unsanctioned apps that have a risk score of 5 or higher and generate more than 200 GB of daily traffic. The solution must minimize administrative effort.
What should you do?


NO.113 Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant.
You have 100 IT administrators who are organized into 10 departments.
You create the access review shown in the exhibit. (Click theExhibittab.)

You discover that all access review requests are received by Megan Bowen.
You need to ensure that the manager of each department receives the access reviews of their respective department.
Solution: You set Reviewers toMember (self).
Does this meet the goal?


NO.114 Your network contains an on-premises Active Directory domain that syncs to an Azure Active Directory (Azure AD) tenant- Users sign in to computers that run Windows 10 and are joined to the domain.
You plan to implement Azure AD Seamless Single Sign-On (Azure AD Seamless SSO).
You need to configure the computers for Azure AD Seamless SSO.
What should you do?


NO.115 You have an Azure subscription that contains the custom roles shown in the following table.

You need to create a custom Azure subscription role named Role3 by using the Azure portal. Role3 will use the baseline permissions of an existing role. Which roles can you clone to create Role3?


NO.116 Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 E5 subscription.
You create a user named User1.
You need to ensure that User1 can update the status of Identity Secure Score improvement actions.
Solution: You assign the Exchange Administrator role to User1.
Does this meet the goal?


NO.117 You have an Azure Active Directory (Azure AD) tenant that contains the following objects:
A device named Device1
Users named User1, User2, User3, User4, and User5
Groups named Group1, Group2, Group3, Group4, and Group5
The groups are configured as shown in the following table.

To which groups can you assign a Microsoft Office 365 Enterprise E5 license directly?


NO.118 Your on-premises network contains an Active Directory domain that uses Azure AD Connect to sync with an Azure AD tenant. You need to configure Azure AD Connect to meet the following requirements:
* User sign-ins to Azure AD must be authenticated by an Active Directory domain controller.
* Active Directory domain users must be able to use Azure AD self-service password reset (SSPR).
What should you use for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.119 You have a Microsoft 365 E5 subscription that contains the users shown in the following table.

The users are assigned the roles shown in the following table.

For which users can User1 and User4 reset passwords? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.120 You configure Azure Active Directory (Azure AD) Password Protection as shown in the exhibit.
(Click the Exhibit tab.)

You are evaluating the following passwords:
– Pr0jectlitw@re
– T@ilw1nd
– C0nt0s0
Which passwords will be blocked?


NO.121 You need to support the planned changes and meet the technical requirements for MFA.
Which feature should you use, and how long before the users must complete the registration? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.122 You have an Azure AD tenant that contains the users shown in the following table.

In Azure AD Identity Protection, you configure a user risk policy that has the following settings:
* Assignments:
o Users: Group1
o User risk: Low and above
* Controls:
o Access: Block access
* Enforce policy: On
In Azure AD Identity Protection, you configure a sign-in risk policy that has the following settings:
* Assignments:
o Users: Group2
o Sign-in risk: Low and above
* Controls:
o Access: Require multi-factor authentication
* Enforce policy. On
the following settings:
ng settings:
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.


SC-300 Dumps and Practice Test (480 Exam Questions): https://www.trainingquiz.com/SC-300-practice-quiz.html

Related Links: myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

Leave a Reply

Please sing in to post your comment or singup if you don't have account.
Enter the text from the image below